AML/CTF compliance features, built for Tranche 2
Every major workflow in duely is designed around the obligations facing Australian accounting firms, real estate agencies, conveyancers, law firms, and jewellers and bullion dealers: program setup, customer onboarding, engagement risk assessment and approval, evidence, suspicious matter handling, and retention.
The screens your team works in
These are real screens from duely, with sample data.
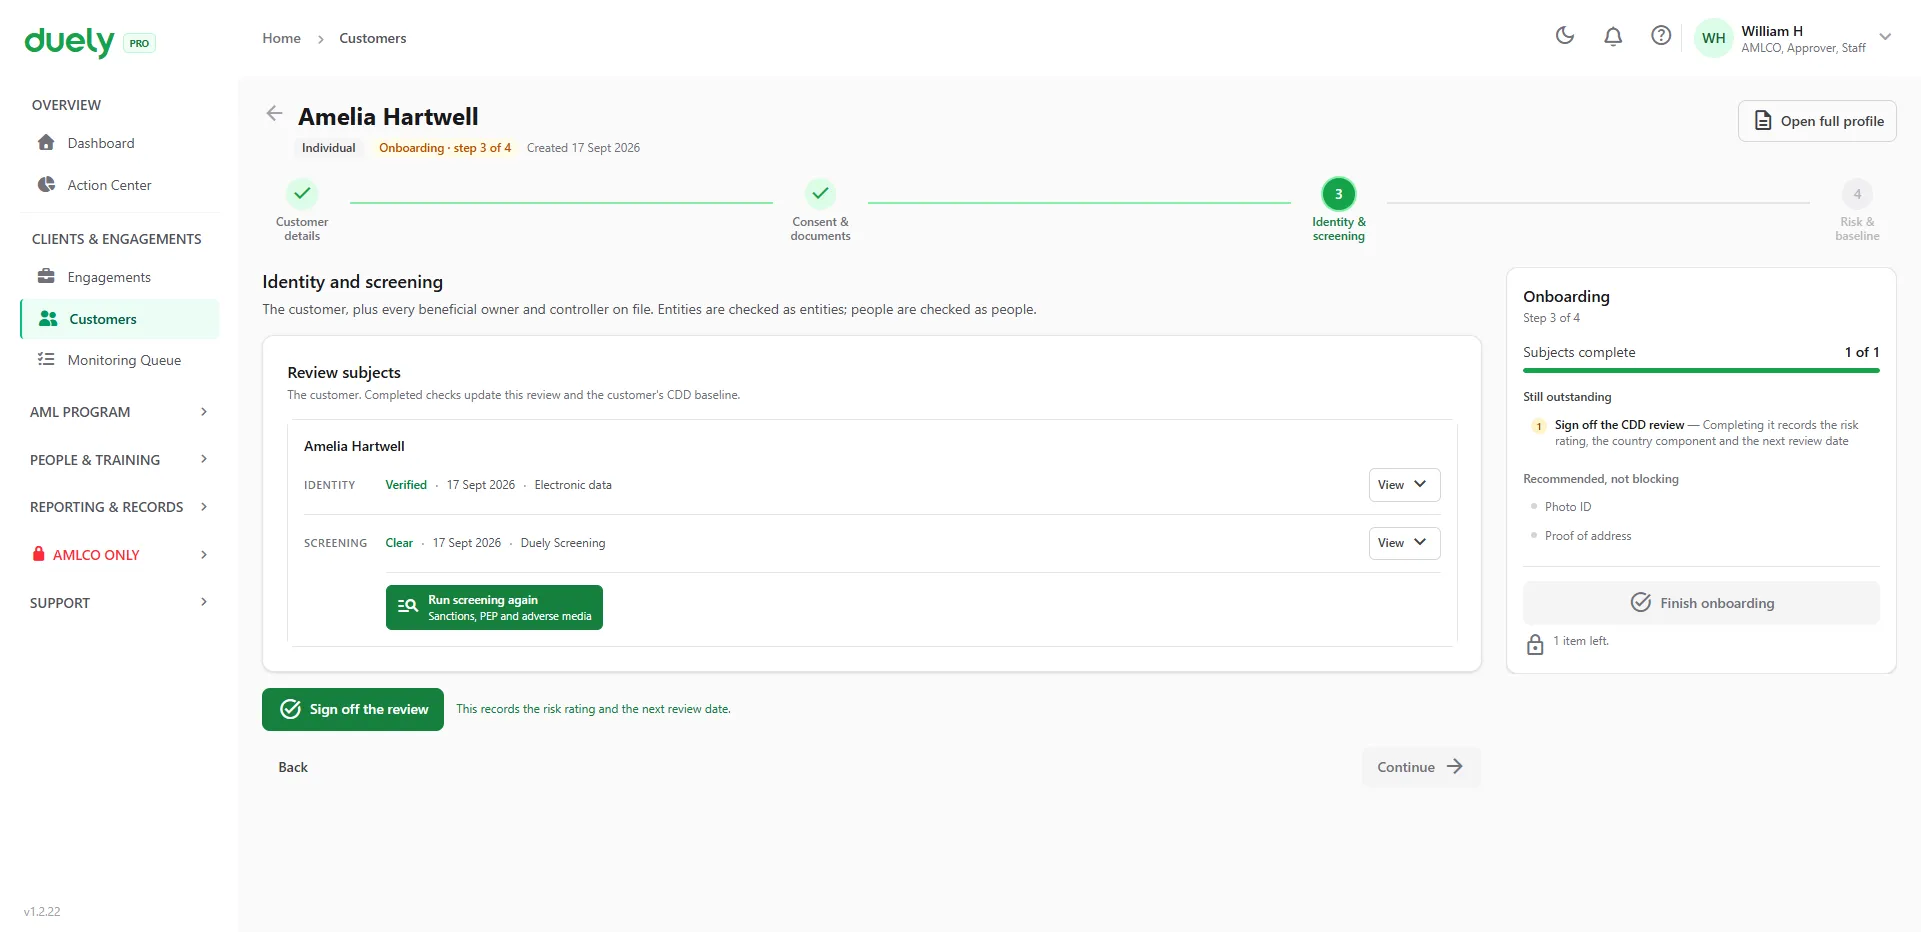
Verify and screen.Identity and screening results sit side by side for each person, with the date and the method used.
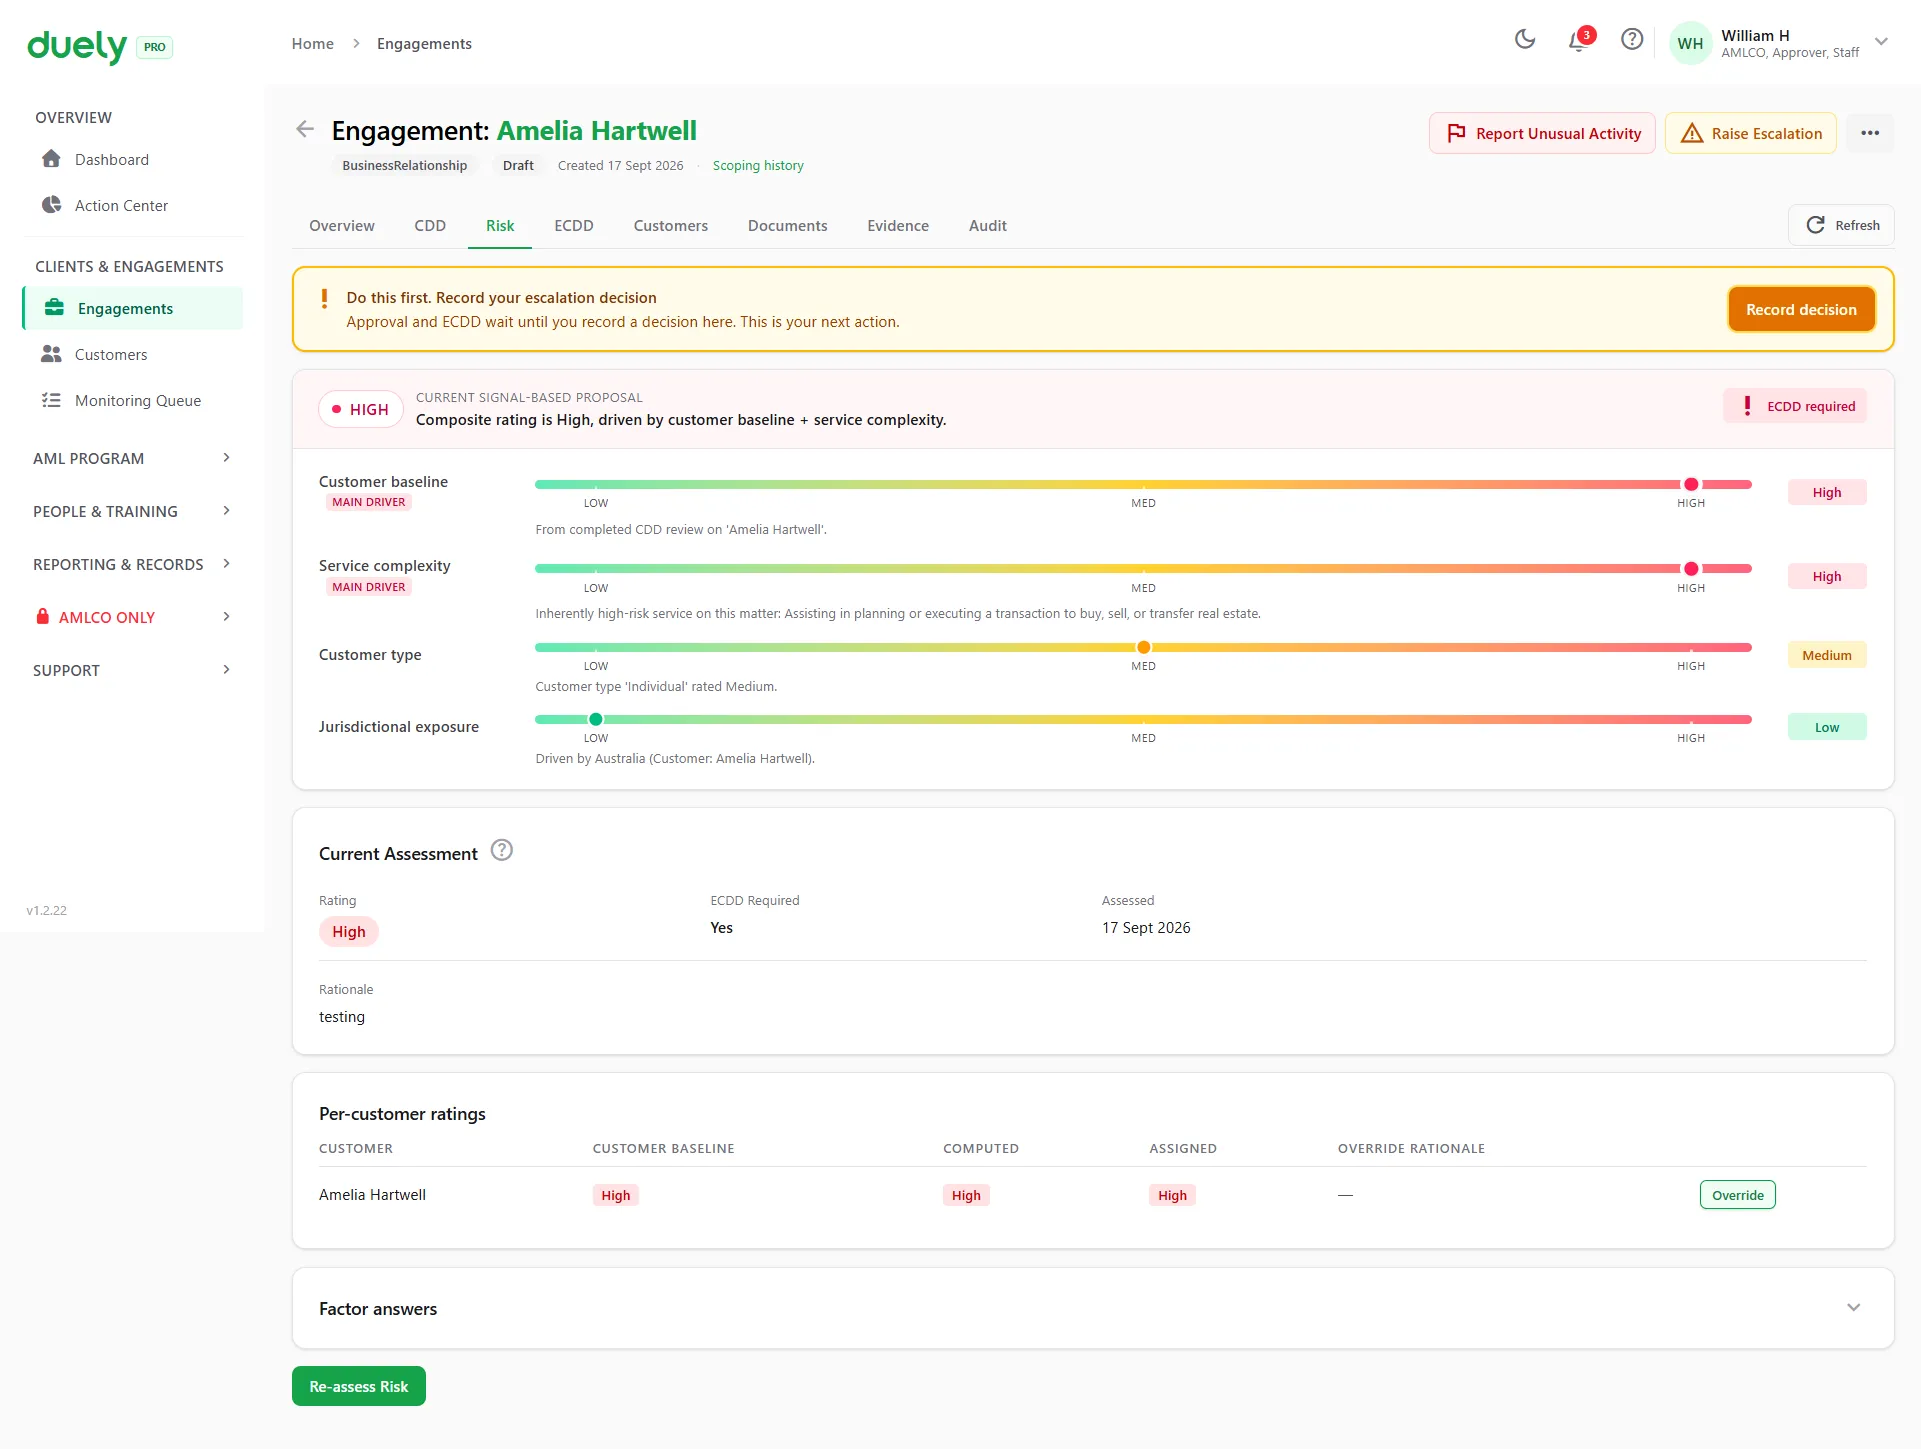
Rate the risk.The answers produce a rating and show what drove it. A High rating opens enhanced due diligence.
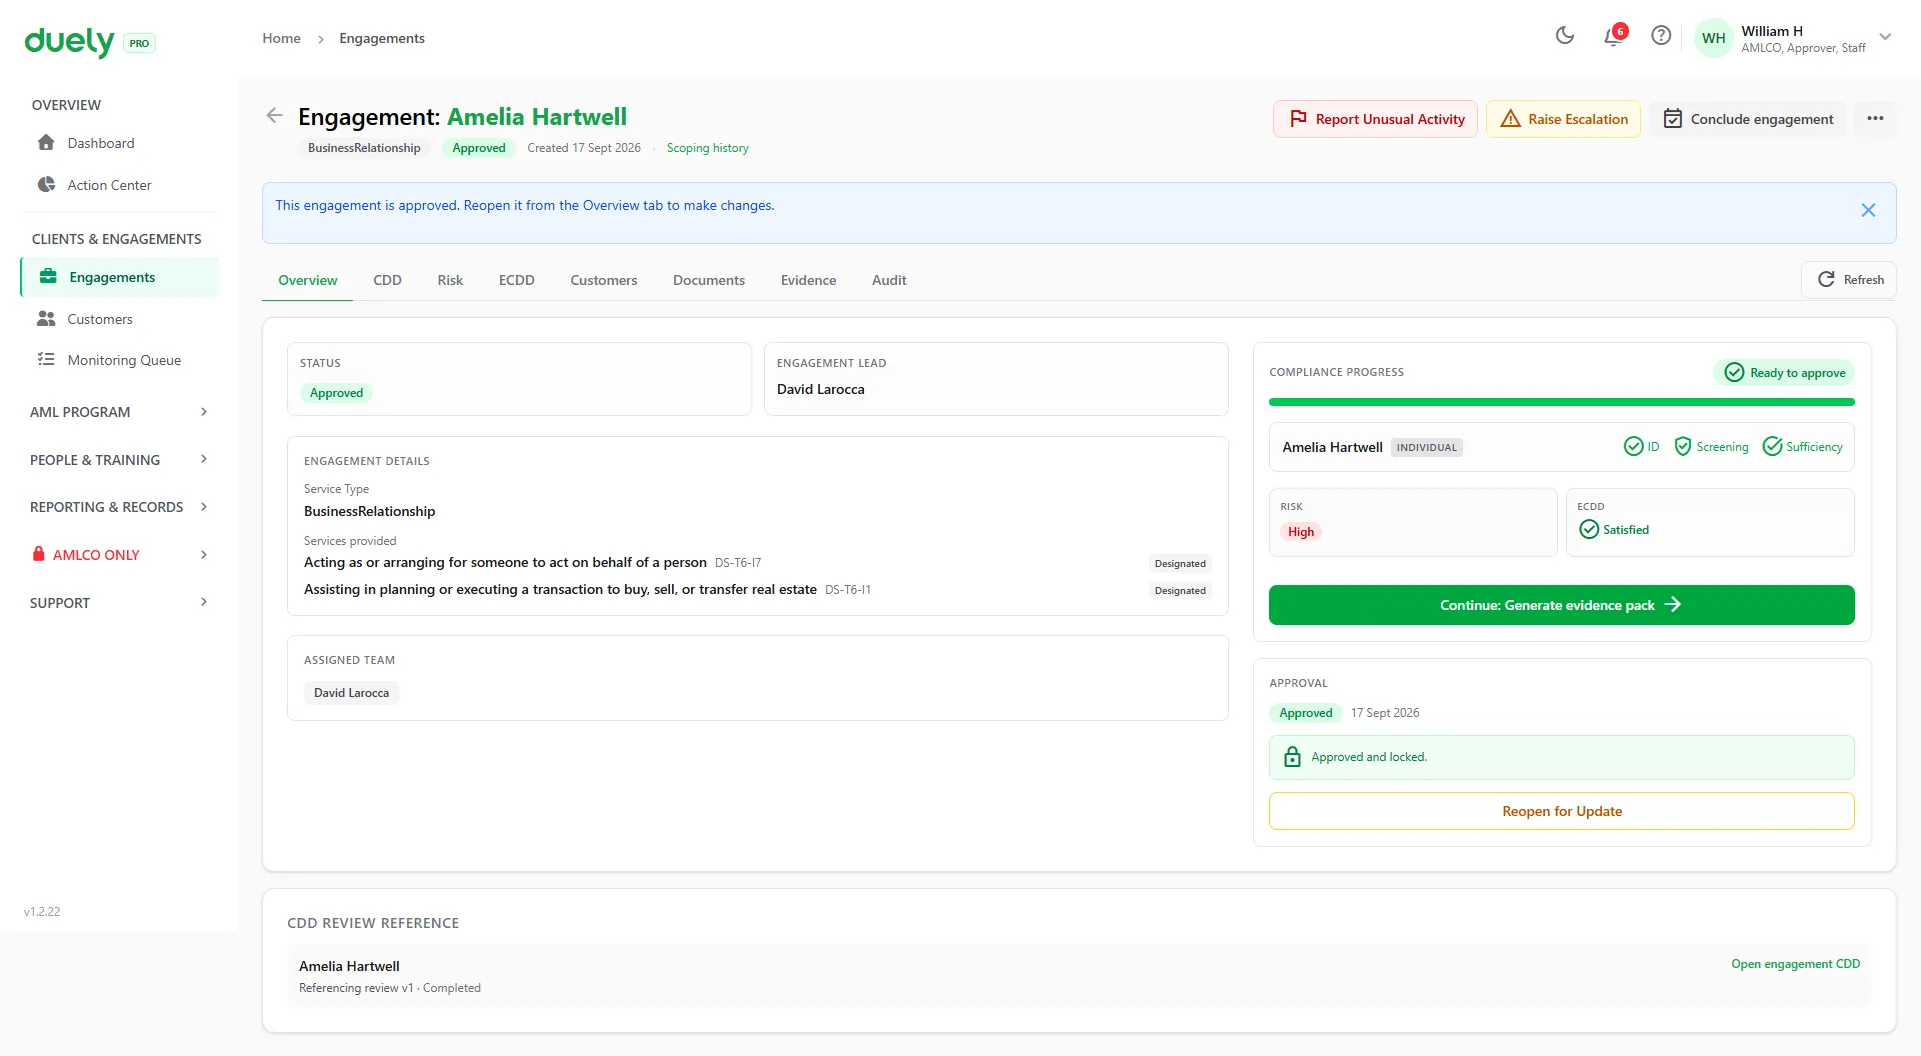
Approve.An approver signs off before the work goes ahead. The approval stays on the record.
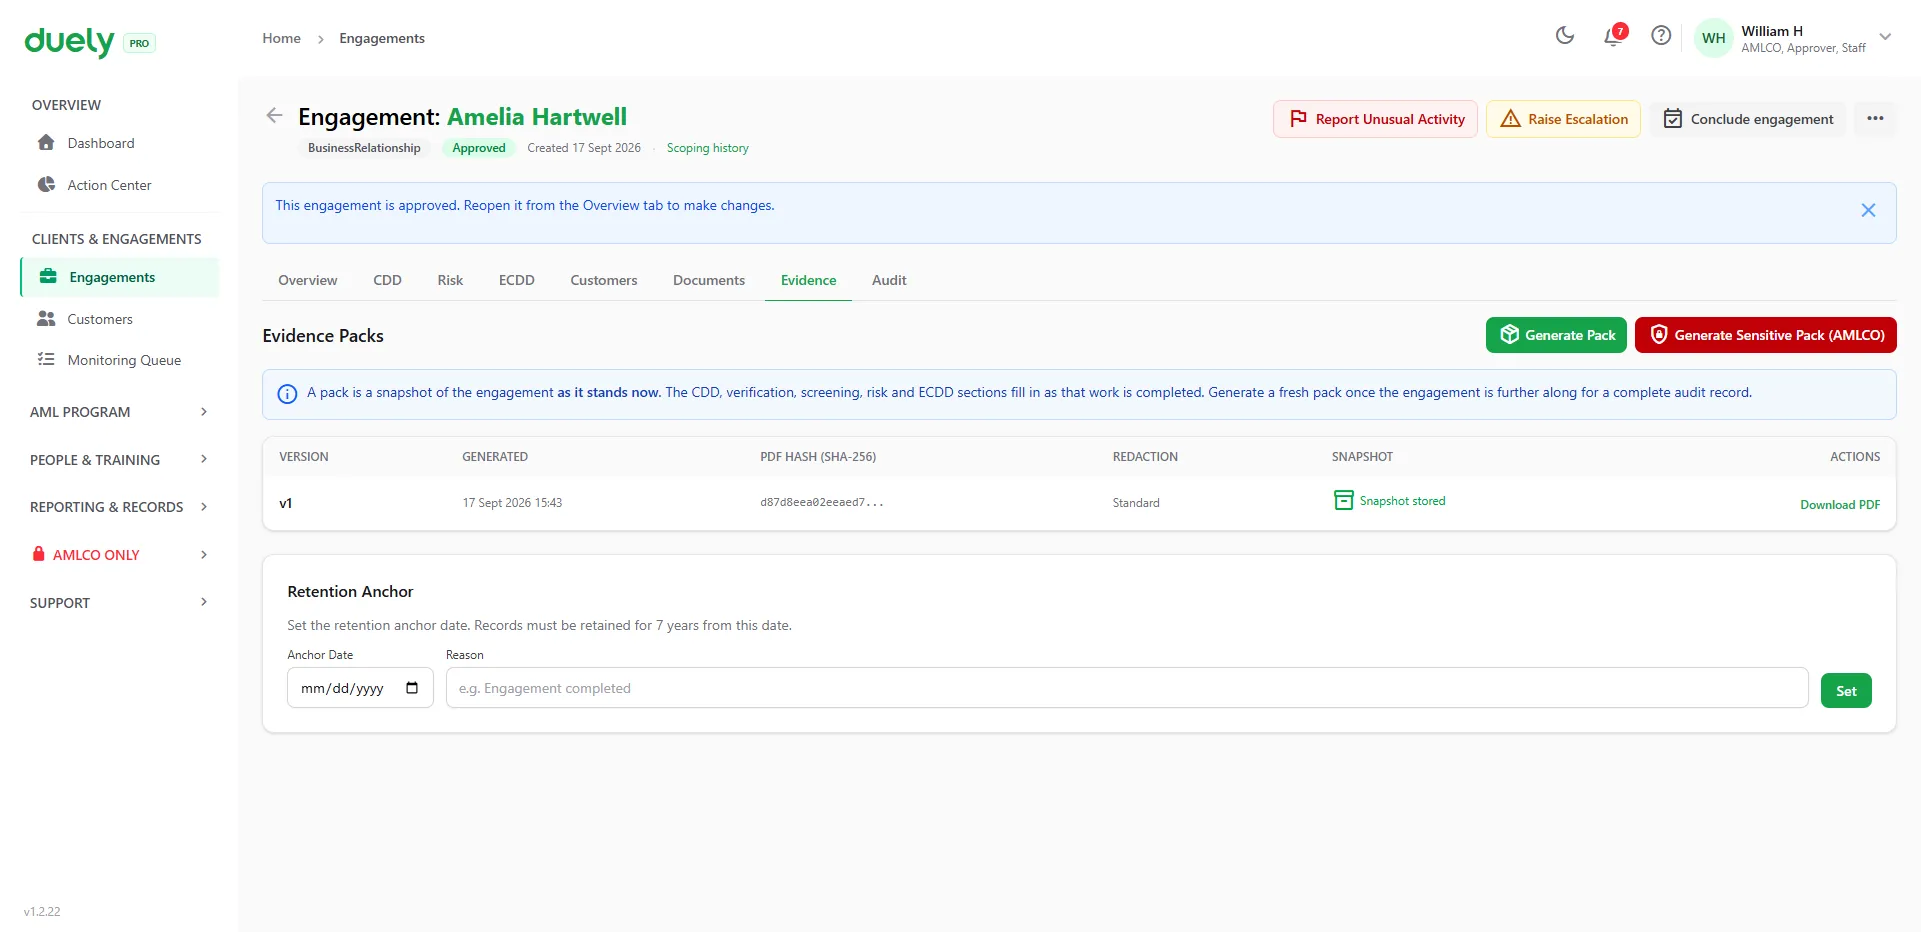
Generate the pack.One PDF, whenever you need it. Each version has its own SHA-256 hash, so any later change to the file can be detected.
Outcome 1
Program and governance
Put in place what your firm needs before its first engagement, and keep it current.
-
AML/CTF program wizard
Build your program with a guided wizard. Each version goes through approval, so the current authorised version is always on file.
-
Versioning and approvals
Every program change is versioned and needs approval, so you have a record of how your program has changed over time.
-
AMLCO appointment
Appoint your AML/CTF compliance officer (AMLCO) with a documented appointment record and role-based access.
-
Training register
Track who has completed AML/CTF training, schedule refreshers, and keep evidence that your training obligations are met.
Outcome 2
Customer and engagement due diligence
Onboard each customer once, then take each engagement through risk assessment to approval.
-
Engagements
Open an engagement for each designated service, add the customers and their roles, and attach existing customer due diligence automatically.
-
Customer and beneficial owner capture
Onboard each customer once, with identity information for beneficial owners, trustees, directors, and controllers.
-
Secure document requests and uploads
Request and receive supporting documents through a secure channel with integrity hashing.
-
Verification workflows
Electronic, documentary, and manual verification paths with structured evidence capture.
-
Screening, risk, and ECDD
Screening against sanctions, PEP and adverse media, guided risk assessment, and enhanced CDD workflows when triggered.
-
Approval workflow
An approver (the AMLCO, or a user with the Approver role) approves every engagement, with documented approver identity and rationale.
See the sanctions, law enforcement and PEP lists customers are checked against, and the countries whose identity documents a customer can verify with.
Outcome 3
Evidence, reporting, and oversight
Turn compliance activity into a usable record and keep oversight across your firm.
-
Evidence pack exports
Generate tamper-evident, versioned evidence packs with SHA-256 hashing and configurable redaction rules.
-
Immutable audit trail
Every action is written to an append-only audit log. Entries cannot be edited or deleted.
-
AMLCO-only SMR handling
Suspicious matter reports are stored in an isolated system, with no sign of them on shared dashboards or in notifications.
-
TTR / IFTI records
Draft records for threshold transaction reports (TTRs) and international funds transfer instructions (IFTIs), with manual attestation.
-
Dashboard, health score, and notifications
A firm-wide view of compliance, with engagement health scores, calendar reminders and team notifications.
What makes duely different
Customer-first, engagement-led workflow
Onboard each customer once and their due diligence attaches to every engagement automatically. Each engagement carries its own approval and evidence pack, plus a risk assessment and ECDD where they apply.
Evidence packs
Once an engagement is approved, generate a versioned, hashed PDF of its record on demand, with nothing to reconstruct by hand.
SMR firewall
Suspicious matter handling is isolated in the architecture: separate data storage, AMLCO-only access, and tipping-off controls on every shared screen.
Explore every feature
Each feature page covers the workflow and the obligation behind it.
Customer-first AML workflow for designated services
duely onboards each customer once, then attaches their due diligence to every engagement automatical...
See the featureGuided identity verification paths with one clear evidence trail
duely supports electronic, documentary and manual verification. Each check records the method, sourc...
See the featureGuided risk assessments with clear escalation to ECDD
duely assesses money laundering and terrorism financing (ML/TF) risk on each engagement using the AU...
See the featureEvidence packs that show what you did, when, and why
duely turns engagement activity into an audit-ready PDF, generated on demand after approval. Each pa...
See the featureThe SMR firewall: tipping-off prevention built into the architecture
Tipping off is a criminal offence under section 123 of the AML/CTF Act, and a policy alone leaves st...
See the featureStructured reporting records for SMR, TTR, and IFTI workflows
duely keeps a structured record for each suspicious matter report (SMR), threshold transaction repor...
See the featureGenerate and maintain your AML/CTF program
duely builds your AML/CTF program from guided inputs, then keeps its versions, approvals, exports an...
See the featureImmutable audit trail across firm and engagement activity
Every major action in duely is added to an append-only audit record with the actor, timestamp, conte...
See the featureYour compliance calendar runs in the background, every day
Scheduled background jobs watch every part of your AML/CTF file that has a deadline. Training curren...
See the featureProve your program keeps working after it has been approved
The reformed AML/CTF regime expects you to keep your program effective and to show your working. due...
See the featureUnusual activity reports the safe step before an SMR
Your staff see things you don't. An unusual activity report (UAR) lets them flag a concern without r...
See the featureReliance in both directions built around s37 and s38
Sections 37 and 38 of the AML/CTF Act let you rely on another reporting entity's customer due dilige...
See the featureBuilt for sensitive data
How duely protects customer and compliance data.
Encryption and secret isolation
Data is encrypted at rest and in transit (TLS 1.2+). Secrets are kept apart from application code, so credentials never appear in source code, configuration or logs.
See security detailsImmutable audit trail
Every action is written to an append-only audit log. Entries cannot be edited or deleted.
See security detailsAustralian data residency
Engagement records and evidence are stored in Australian data centres. Identity and biometric checks and screening are performed by specialist providers outside Australia, and the evidence is stored in Australia.
See security detailsExplore the workflow in detail
Follow the four stages in duely from first customer to approved engagement, or check which obligations apply to your firm.